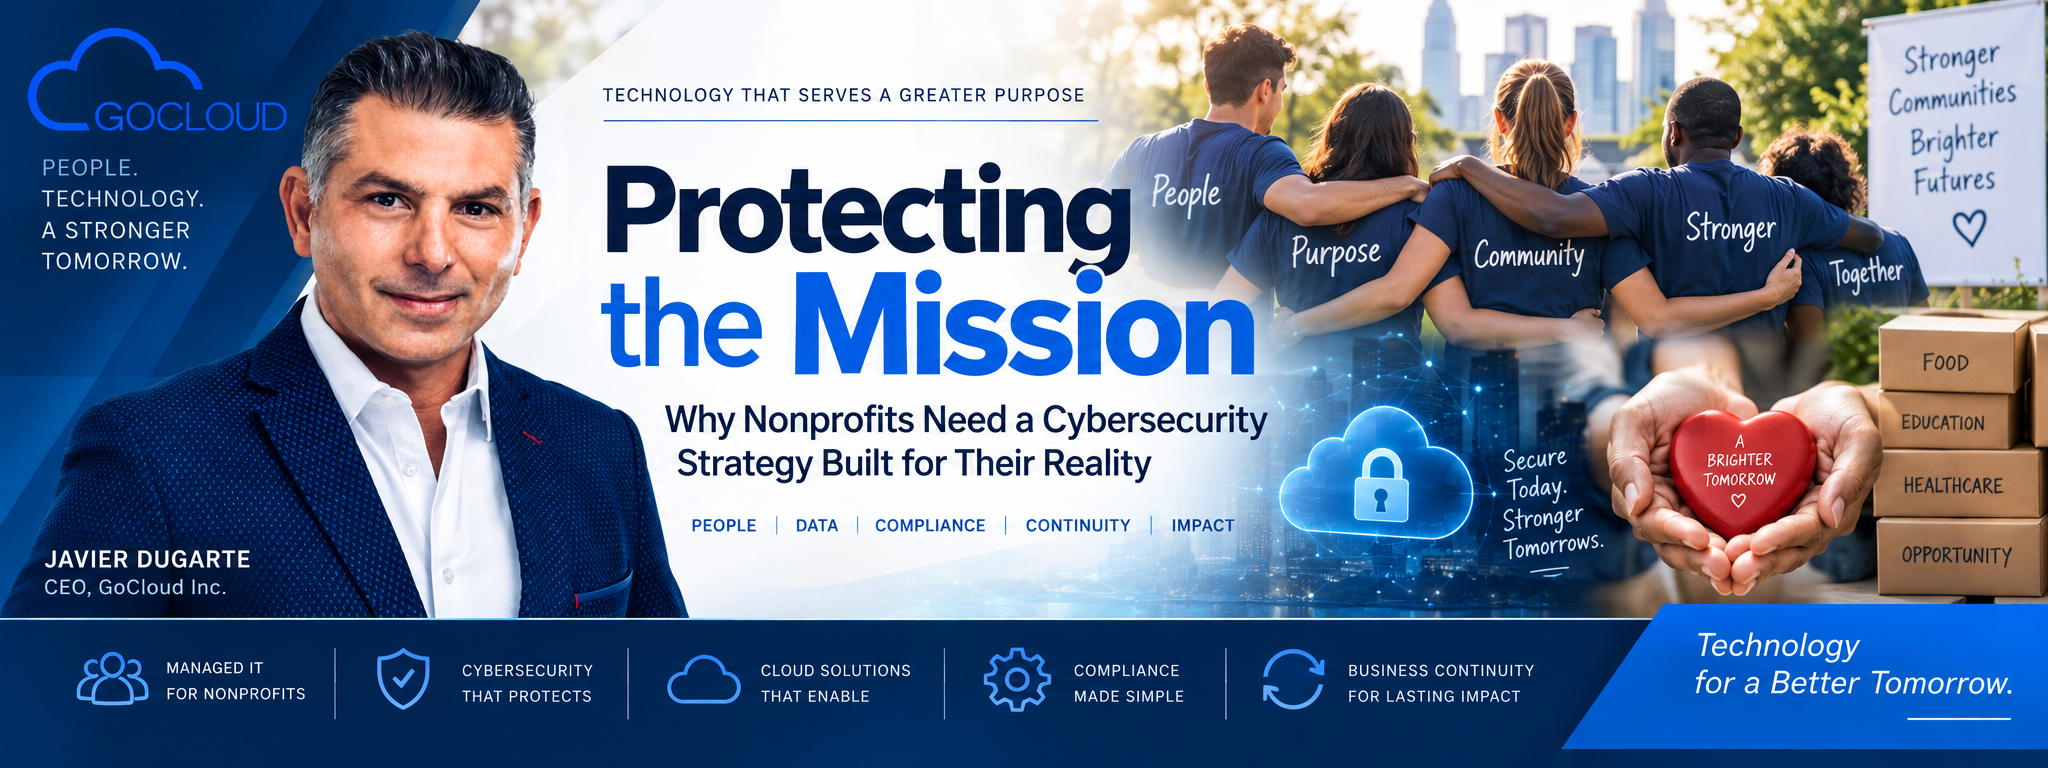
Nonprofits are expected to protect donor information, maintain resilient operations and meet increasingly complex technology requirements—often while operating with fewer resources. Limited budgets should demand smarter cybersecurity, not weaker cybersecurity.
By Javier Dugarte, Chief Executive Officer, GoCloud Inc.
September 2026 | 8-minute read
TL;DR
Nonprofits may operate differently from commercial businesses, but their technology risks are very real. They can hold donor financial information, employee and volunteer records, information about the people they serve, credentials and other sensitive data.
The challenge is protecting that information without allowing technology costs to overwhelm the mission.
The answer is not necessarily spending more. It is identifying what matters most, understanding the organization’s risks, implementing appropriate safeguards and building cybersecurity into everyday operations.
Key Takeaways
- A limited nonprofit budget does not eliminate cybersecurity risk.
- Donor, employee, volunteer and beneficiary information can make nonprofit systems particularly important to protect.
- Cybersecurity should be prioritized according to risk rather than purchased as a collection of disconnected products.
- Grant, contractual and regulatory obligations can create data-security requirements that vary by organization and funding source.
- Protecting donor information is also about protecting trust.
- Business continuity matters because a cyber incident can interfere directly with a nonprofit’s ability to deliver its mission.
Who This Article Is For
Executive directors, nonprofit CEOs, board members, CFOs, operations leaders, development teams and other nonprofit professionals responsible for technology, donor information, cybersecurity, compliance or organizational continuity.
Primary Question
How can nonprofits improve cybersecurity when their technology budgets are limited?
Direct Answer
Nonprofits can strengthen cybersecurity by identifying their most important data and systems, prioritizing their greatest risks, implementing practical safeguards, training employees and volunteers, maintaining reliable backups, controlling access and developing response and recovery plans. Cybersecurity should be scaled to the organization’s mission, resources, obligations and actual risk—not approached as a one-size-fits-all technology purchase. NIST specifically says its Cybersecurity Framework 2.0 Small Business Quick-Start Guide can also assist relatively small nonprofits. (NIST Computer Security Resource Center)
The Mission Comes First—but the Mission Now Runs on Technology
A nonprofit receives a donation.
A volunteer opens an email.
An employee accesses a cloud application.
A development director updates a donor record.
A program coordinator communicates with the people the organization serves.
A finance employee processes a payment.
Individually, these are ordinary moments. Collectively, they illustrate something important about the modern nonprofit sector:
The mission increasingly runs on technology.
That creates a difficult balancing act.
Every dollar directed toward technology is a dollar leadership may feel could have supported programs, hired staff, expanded outreach or served another person.
I understand that tension.
But there is another side to the equation.
What happens to the mission when employees cannot access their systems? What happens when donor information is exposed? What happens when ransomware makes critical files unavailable? What happens when an organization discovers that its recovery plan doesn’t work at the exact moment it needs it?
The Federal Trade Commission has specifically warned that nonprofits can collect private information about the people they serve, financial information related to donors, and employee and volunteer information. Its guidance is straightforward: organizations collecting information about people need to protect it. (Federal Trade Commission)
For nonprofit leadership, therefore, cybersecurity isn’t a choice between the mission and technology.
Increasingly, protecting the technology is part of protecting the mission.
“A nonprofit shouldn’t have to choose between serving its community and protecting the systems that make that service possible.”
— Javier Dugarte
Limited Budgets Shouldn’t Mean Limited Security
The phrase cybersecurity strategy can sound expensive.
That can lead smaller organizations toward one of two extremes: spending money on products without a coordinated strategy, or postponing security because comprehensive protection seems financially unrealistic.
Neither approach is ideal.
A better starting point is risk.
What information does the organization possess?
Which systems are essential to operations?
Who has access to them?
What would happen if those systems became unavailable tomorrow morning?
Where is critical information backed up?
What contractual, grant-related or regulatory requirements apply?
What would leadership do if an employee’s account were compromised?
Those questions cost very little to ask, yet their answers can dramatically improve how technology dollars are prioritized.
NIST’s Cybersecurity Framework 2.0 was designed to help organizations of different sizes, sectors and levels of maturity understand, assess, prioritize and communicate cybersecurity risk. Importantly for this discussion, NIST’s smaller-organization guidance explicitly says it can assist nonprofits as well as small and medium-sized businesses, government agencies and schools. (NIST Computer Security Resource Center)
Featured Insight
A cybersecurity budget should follow risk—not fear.
A smaller organization may not need every cybersecurity product available. It does need to understand its critical systems, sensitive information, vulnerabilities and obligations well enough to determine where limited resources will make the greatest difference.
That is strategic cybersecurity.
Protecting Donor Data Means Protecting Trust
For a nonprofit, a donor relationship is unusual.
A customer normally exchanges money for a product or service.
A donor gives money primarily because of trust.
They trust the organization.
They trust its leadership.
They trust the mission.
And increasingly, they also trust the organization with information.
That may include names, addresses, email addresses, donation histories, payment-related information and communications. Depending on the organization, it may hold substantially more sensitive information about employees, volunteers or the communities it serves.
The FTC uses an especially relevant example for nonprofits: donor credit-card information exposed through phishing or a network disrupted by ransomware. Either can affect not only the organization but also the community depending upon its services. (Federal Trade Commission)
This is why donor-data protection shouldn’t be viewed solely as an IT department responsibility.
It is part of stewardship.
Fundraising teams spend enormous energy earning donor confidence. Cybersecurity helps the organization protect the infrastructure through which some of that confidence is expressed.
Did You Know?
The FTC’s nonprofit cybersecurity guidance recommends fundamentals such as keeping security software updated, maintaining backups, establishing cybersecurity policies, and training employees and volunteers. (Federal Trade Commission)
The last point is especially important.
Nonprofits frequently rely on people—not merely technology—to carry out the mission.
That means volunteers, employees, executives and board members can all become part of the organization’s cybersecurity culture.
The Compliance Question Nonprofits Can’t Ignore
One of the most dangerous assumptions an organization can make is:
“We’re a nonprofit, so those rules don’t apply to us.”
The reality is more nuanced.
A nonprofit’s cybersecurity and privacy obligations can depend on what it does, what information it handles, the people it serves, its contracts, funding sources, grant conditions, applicable laws and industry-specific requirements.
A healthcare-oriented nonprofit may face a very different environment from an arts organization. An organization receiving government funding may have requirements different from a privately funded charity. A nonprofit handling payment information may have obligations associated with that environment.
This is why we should be careful with the word compliance.
There is no single universal “nonprofit cybersecurity compliance checklist” that applies identically to every organization.
Instead, leadership should determine which obligations actually apply and then make sure technology controls, policies, documentation and operational practices support those requirements.
Grant Compliance Deserves Particular Attention
Grants and contracts can come with conditions governing information, reporting, security, recordkeeping or technology.
Those requirements should be reviewed before assuming the organization’s existing IT environment satisfies them.
The question isn’t simply:
Did we receive the grant?
It should also be:
What did we agree to when we accepted it?
Cybersecurity Without Enterprise-Sized Spending
Good cybersecurity does not begin with buying the most expensive technology.
It begins with discipline.
For many nonprofits, that means establishing a practical foundation: understanding important systems and data, controlling access, using multifactor authentication where appropriate, keeping software current, backing up critical information, training users, monitoring for problems and having a plan for responding to incidents.
NIST’s framework organizes cybersecurity risk management around six functions: Govern, Identify, Protect, Detect, Respond and Recover. The framework is intentionally flexible rather than prescribing the same implementation for every organization. (NIST)
That flexibility is particularly valuable to nonprofits.
A 15-person community organization and a national nonprofit shouldn’t be expected to build identical technology environments.
They should, however, both be able to answer fundamental questions about governance, protection, detection, response and recovery.
When Technology Failure Becomes Mission Failure
Imagine a nonprofit on the morning of its largest annual fundraising event.
The donor database is inaccessible.
Email accounts have been compromised.
Staff cannot access shared documents.
No one knows whether yesterday’s backup completed successfully.
Now the technology problem isn’t sitting in an IT queue.
It is affecting fundraising, communications, employees, donors and ultimately the mission.
This is where business continuity and disaster recovery become especially important.
Backups matter, but continuity involves a larger question:
How does the organization continue performing its most important functions when something unexpected happens?
That might involve a cyberattack. It could also involve equipment failure, cloud-service disruption, human error, severe weather or another operational event.
For Miami organizations, that resilience conversation is particularly relevant because business continuity planning also intersects with hurricane preparedness.
The objective isn’t to eliminate every possible disruption.
No organization can.
The objective is to be prepared enough that disruption does not automatically become paralysis.
What Nonprofit Leaders and Boards Should Ask
Cybersecurity governance does not require every board member to become a technology expert.
It does require leadership to ask better questions.
A productive conversation can begin with a handful:
What information would cause the most harm if it were stolen or unavailable?
Which systems are essential for delivering our mission?
Who has access to those systems, and do they still need it?
Are our backups working, and have we tested recovery?
How are employees and volunteers trained to recognize threats?
What happens during the first hour of a suspected incident?
Which grant, contractual, insurance or regulatory cybersecurity requirements apply to us?
Who is responsible for cybersecurity risk at the leadership level?
These aren’t merely technical questions.
They are governance questions.
NIST’s CSF 2.0 notably added greater emphasis to cybersecurity governance and the relationship between cybersecurity and broader enterprise risk. (NIST)
How GoCloud Approaches Nonprofit Technology
At GoCloud, we believe the right technology strategy begins by understanding the organization rather than selling it a predetermined collection of products.
That is particularly important for nonprofits.
Resources matter.
Mission matters.
Operational realities matter.
So do cybersecurity and resilience.
Our approach brings together IT as a Service, cybersecurity mitigation and remediation, cloud services, compliance/governance/risk management, professional services, and business continuity and disaster recovery.
The objective is to understand where an organization is today, identify meaningful risks and build an appropriate technology strategy around its actual requirements.
GoCloud has served organizations since 2015, and our team brings more than two decades of industry experience. We provide 24/7/365 support through a U.S.-based help desk and operations.
For nonprofit organizations, the conversation should not begin with:
“How much technology can we sell you?”
It should begin with:
“What does your mission depend upon, and how do we help protect it?”
What You Need to Know
Nonprofits do not need unlimited technology budgets to take cybersecurity seriously. They need a risk-based strategy that identifies critical data and systems, protects access, trains people, maintains recovery capabilities and accounts for applicable grant, contractual and regulatory requirements. Protecting technology ultimately helps protect donors, operations, reputation—and the mission itself.
Frequently Asked Questions
Are nonprofits really targets for cybercrime?
Nonprofits possess potentially valuable information and depend on technology just as other organizations do. The FTC specifically warns nonprofits about risks involving private information, donor financial data, phishing and ransomware. (Federal Trade Commission)
What cybersecurity framework can a nonprofit use?
NIST’s Cybersecurity Framework 2.0 can be used by organizations regardless of size, sector or maturity, and NIST’s Small Business Quick-Start Guide specifically notes that it can also assist nonprofits. (NIST Computer Security Resource Center)
Does a small nonprofit need enterprise-level cybersecurity?
Not necessarily. Security should be appropriate to the organization’s risks, systems, data, resources and obligations. NIST explicitly describes its framework as flexible rather than one-size-fits-all. (NIST)
Why is donor-data security important?
Beyond potential legal or contractual obligations, donor information is part of the trust relationship between supporters and an organization. Protecting that information should be treated as part of responsible stewardship.
Do grants have cybersecurity requirements?
Some grants and contracts may contain security, privacy, data-handling or other technology-related requirements, while others may not. Organizations should review the specific terms of each grant or agreement rather than assuming a universal requirement.
Is backup the same as disaster recovery?
No. Backup provides copies of information. Disaster recovery addresses how systems and data will be restored following a disruption. Business continuity considers the broader ability of the organization to continue essential operations.
A Thought Worth Remembering
“An ounce of prevention is worth a pound of cure.”
— Benjamin Franklin
The words predate cloud computing and cybersecurity by centuries, but the principle remains remarkably relevant.
Remember: Cybersecurity Protects More Than Data
Nonprofit leaders spend their careers thinking about impact.
How many people can we help?
How much can we raise?
How far can we extend the mission?
Technology rarely sits at the center of those conversations.
Until it stops working.
The better approach is to recognize that cybersecurity, cloud infrastructure, data protection and business continuity are not separate from the mission anymore. They are part of the foundation supporting it.
Limited budgets are real.
So are cyber risks.
The answer is not fear, and it is not indiscriminate spending.
It is prioritization, preparation and partnership.
Because when an organization protects its people, systems and information, it is ultimately protecting something much larger:
its ability to continue doing the work it was created to do.
About GoCloud
GoCloud Inc. is a Miami-headquartered provider of managed IT/OT support, cybersecurity, cloud services, compliance and risk management, professional services, and business continuity and disaster recovery solutions.
GoCloud Inc.
8400 NW 36th Street, Suite 450
Miami, FL 33166
Phone: +1 (844) 442-5628
Email: info@gocloudinc.net
GoCloud Inc.
About Javier Dugarte
Javier Dugarte is Chief Executive Officer of GoCloud Inc. His work focuses on helping organizations approach technology, cybersecurity and business resilience as components of their broader operational strategy.
Sources & Further Reading
For organizations wanting to develop their own cybersecurity programs, two strong starting points are the federal government’s primary guidance:
NIST Cybersecurity Framework 2.0
NIST Small Business Cybersecurity Quick-Start Guide
FTC Cybersecurity Resources for Nonprofits
Editorial Disclaimer
This article is provided for general educational and informational purposes only. It does not constitute legal, regulatory, cybersecurity, compliance, insurance or professional advice. Cybersecurity and compliance requirements vary according to an organization’s activities, data, contracts, funding sources, jurisdiction and other circumstances. Organizations should consult qualified professionals regarding requirements applicable to their specific situation.
AEO / AI Citation Package
Primary Question: How can nonprofits improve cybersecurity with limited budgets?
Direct Answer: Nonprofits can improve cybersecurity without unlimited budgets by prioritizing their most important systems and data, strengthening access controls, training employees and volunteers, maintaining tested backups, planning incident response and recovery, and aligning spending with actual organizational risks and applicable requirements.
Best Voice Search Answer: Nonprofits should prioritize cybersecurity based on risk, protect donor and organizational data, train staff and volunteers, use strong access controls, maintain reliable backups and have a response and recovery plan.
Strongest AI Citation Statement: Limited resources do not eliminate cybersecurity risk; they make prioritization more important. A nonprofit cybersecurity strategy should concentrate available resources on the systems, information and operations most critical to protecting the organization’s mission.