Select Page

Communities

Widgetized Area

This panel is active and ready for you to add some widgets via the WP Admin

North Bay Village, Florida, offers a selection of accommodations to suit various preferences and budgets. Here are some hotels in and around the area:

North Bay Village, FL

A midscale, smoke-free hotel featuring a heated outdoor swimming pool, exercise room, and on-site restaurant and lounge. Conveniently located 12 miles from Miami Airport.

North Bay Village, FL

A clean and safe accommodation option with street parking, located 20 minutes from Miami. Guests appreciate its convenient location and friendly staff.

North Bay Village, FL

Offers spacious apartments with excellent views of Biscayne Bay, easy parking, and a well-equipped kitchen. Ideal for families and longer stays.

North Bay Village, FL

Provides large rooms with comfortable accommodations, including kitchen facilities. Guests enjoy the home-like atmosphere and good cleaning service.

North Bay Village, FL

Offers budget-friendly accommodations with basic amenities. Some guests have noted areas for improvement in cleanliness and maintenance.

These options provide a range of amenities and price points to cater to different traveler needs in North Bay Village.
Missoni Opens New Boutique at Aventura Mall

Aventura Mall has added another fashion name to its roster of luxury retailers, with Italian design house Missoni opening a new boutique at the Aventura shopping center. The opening was marked with a celebration hosted by Haute Living, drawing fashion enthusiasts, brand representatives and members of the local business community to the mall’s luxury wing.
Missoni, known internationally for its signature zigzag knitwear, colorful patterns and Italian craftsmanship, joins a growing lineup of high-end labels that have chosen Aventura as their South Florida home base. The brand’s arrival continues a trend of European fashion houses expanding into the Aventura market, where a mix of year-round residents, seasonal visitors and international shoppers has made the mall one of the highest-performing retail properties in the country.
For the Aventura area, each new luxury tenant carries practical benefits beyond the storefront itself. Boutique openings typically bring retail jobs, visual merchandising work, and increased foot traffic that supports neighboring restaurants, cafes and service businesses inside and around the mall. Aventura Mall remains a significant contributor to the city’s tax base and a primary driver of the local economy, and additions like Missoni help reinforce its position as a destination shopping center rather than a purely regional one.
The celebration format itself has become a familiar part of Aventura’s retail calendar. Brand launch events bring together local business owners, designers and community members, offering a look at new collections while giving Aventura businesses another reason to be part of the conversation around South Florida luxury retail. Residents interested in seeing the new boutique can visit Aventura Mall during regular shopping hours, where Missoni’s collection of ready-to-wear, accessories and home goods is now available.
For a city of roughly 40,000 residents, Aventura’s retail profile continues to punch well above its size. The steady arrival of internationally recognized brands signals ongoing confidence in the Aventura market and gives local shoppers access to labels that might otherwise require a trip to New York, Milan or Paris.
Source: Haute Living

This article was AI-generated from public sources & humanized (occasionally edits). MiamiBusiness.com is committed to transparent AI journalism. Please verify with original outlets.

Read More

The Nonprofit Cybersecurity Paradox: Protecting the Mission When Every Dollar Matters

Nonprofits are expected to protect donor information, maintain resilient operations and meet increasingly complex technology requirements—often while operating with fewer resources. Yet limited budgets should demand smarter cybersecurity, not weaker cybersecurity.

By Javier Dugarte, Chief Executive Officer, GoCloud Inc. September 2026 | 8-minute read
TL;DR
Nonprofits may operate differently from commercial businesses, but their technology risks are very real. In practice, they can hold donor financial information, employee and volunteer records, information about the people they serve, credentials and other sensitive data.
The challenge, therefore, is protecting that information without allowing technology costs to overwhelm the mission.
Fortunately, the answer is not necessarily spending more. Instead, it is identifying what matters most, understanding the organization’s risks, implementing appropriate safeguards and building cybersecurity into everyday operations.
Key Takeaways A limited nonprofit budget does not eliminate cybersecurity risk. Because nonprofits hold donor, employee, volunteer and beneficiary information, their systems can be particularly important to protect. Cybersecurity should be prioritized according to risk rather than purchased as a collection of disconnected products. In addition, grant, contractual and regulatory obligations can create data-security requirements that vary by organization and funding source. Ultimately, protecting donor information is also about protecting trust. Business continuity matters because a cyber incident can interfere directly with a nonprofit’s ability to deliver its mission. Who This Article Is For
Executive directors, nonprofit CEOs, board members, CFOs, operations leaders, development teams and other nonprofit professionals responsible for technology, donor information, cybersecurity, compliance or organizational continuity.
Primary Question
How can nonprofits improve cybersecurity when their technology budgets are limited?
Direct Answer
Nonprofits can strengthen cybersecurity by identifying their most important data and systems, prioritizing their greatest risks, implementing practical safeguards, training employees and volunteers, maintaining reliable backups, controlling access and developing response and recovery plans. Above all, cybersecurity should be scaled to the organization’s mission, resources, obligations and actual risk—not approached as a one-size-fits-all technology purchase. Notably, NIST says its Cybersecurity Framework 2.0 Small Business Quick-Start Guide can also assist relatively small nonprofits.
The Mission Comes First—but the Mission Now Runs on Technology
A nonprofit receives a donation.
Then a volunteer opens an email.
An employee accesses a cloud application.
Meanwhile, a development director updates a donor record.
Elsewhere, a program coordinator communicates with the people the organization serves.
Finally, a finance employee processes a payment.
Individually, these are ordinary moments. Collectively, however, they illustrate something important about the modern nonprofit sector:
The mission increasingly runs on technology.
That, in turn, creates a difficult balancing act.
Every dollar directed toward technology is a dollar leadership may feel could have supported programs, hired staff, expanded outreach or served another person.
I understand that tension.
But there is another side to the equation.
What happens to the mission when employees cannot access their systems? How does the organization respond when donor information is exposed? And what if ransomware makes critical files unavailable? Worse still, imagine discovering that the recovery plan doesn’t work at the exact moment it is needed.
Moreover, the Federal Trade Commission has specifically warned that nonprofits can collect private information about the people they serve, financial information related to donors, and employee and volunteer information. Its guidance is straightforward: in short, organizations collecting information about people need to protect it.
For nonprofit leadership, therefore, cybersecurity isn’t a choice between the mission and technology.
Increasingly, protecting the technology is part of protecting the mission.
“A nonprofit shouldn’t have to choose between serving its community and protecting the systems that make that service possible.”
— Javier Dugarte
Limited Budgets Shouldn’t Mean Limited Security
The phrase cybersecurity strategy can sound expensive.
As a result, that perception can lead smaller organizations toward one of two extremes: spending money on products without a coordinated strategy, or postponing security because comprehensive protection seems financially unrealistic.
Unfortunately, neither approach is ideal.
A better starting point, therefore, is risk.
What information does the organization possess?
Which systems are essential to operations?
Who has access to them?
What would happen if those systems became unavailable tomorrow morning?
Where is critical information backed up?
What contractual, grant-related or regulatory requirements apply?
Finally, what would leadership do if an employee’s account were compromised?
Those questions cost very little to ask, yet their answers can dramatically improve how technology dollars are prioritized.
Similarly, NIST’s Cybersecurity Framework 2.0 was designed to help organizations of different sizes, sectors and levels of maturity understand, assess, prioritize and communicate cybersecurity risk. Importantly for this discussion, NIST’s smaller-organization guidance explicitly says it can assist nonprofits as well as small and medium-sized businesses, government agencies and schools.
Featured Insight
A cybersecurity budget should follow risk—not fear.
A smaller organization may not need every cybersecurity product available. It does, however, need to understand its critical systems, sensitive information, vulnerabilities and obligations well enough to determine where limited resources will make the greatest difference.
That, in short, is strategic cybersecurity.
Protecting Donor Data Means Protecting Trust
For a nonprofit, a donor relationship is unusual.
A customer normally exchanges money for a product or service.
A donor, by contrast, gives money primarily because of trust.
They trust the organization.
Likewise, they believe in its leadership.
Above all, they trust the mission.
And increasingly, they also trust the organization with information.
That may include names, addresses, email addresses, donation histories, payment-related information and communications. Depending on the organization, moreover, it may hold substantially more sensitive information about employees, volunteers or the communities it serves.
For example, the FTC points to donor credit-card information exposed through phishing, or a network disrupted by ransomware. Either scenario can affect not only the organization but also the community depending upon its services.
This is why donor-data protection shouldn’t be viewed solely as an IT department responsibility.
Rather, it is part of stewardship.
Fundraising teams spend enormous energy earning donor confidence. Cybersecurity, in turn, helps the organization protect the infrastructure through which some of that confidence is expressed.
Did You Know?
The FTC’s nonprofit cybersecurity guidance recommends fundamentals such as keeping security software updated, maintaining backups, establishing cybersecurity policies, and training employees and volunteers.
That last point is especially important.
After all, nonprofits frequently rely on people—not merely technology—to carry out the mission.
As a result, volunteers, employees, executives and board members can all become part of the organization’s cybersecurity culture.
The Compliance Question Nonprofits Can’t Ignore
One of the most dangerous assumptions an organization can make is:
“We’re a nonprofit, so those rules don’t apply to us.”
In reality, the situation is more nuanced.
A nonprofit’s cybersecurity and privacy obligations can depend on what it does, what information it handles, the people it serves, its contracts, funding sources, grant conditions, applicable laws and industry-specific requirements.
For example, a healthcare-oriented nonprofit may face a very different environment from an arts organization. Similarly, an organization receiving government funding may have requirements different from a privately funded charity. Meanwhile, a nonprofit handling payment information may have obligations associated with that environment.
This is why we should be careful with the word compliance.
Indeed, there is no single universal “nonprofit cybersecurity compliance checklist” that applies identically to every organization.
Instead, leadership should determine which obligations actually apply and then make sure technology controls, policies, documentation and operational practices support those requirements.
Grant Compliance Deserves Particular Attention
Grants and contracts can come with conditions governing information, reporting, security, recordkeeping or technology.
Those requirements should therefore be reviewed before assuming the organization’s existing IT environment satisfies them.
The question isn’t simply:
Did we receive the grant?
It should also be:
What did we agree to when we accepted it?
Cybersecurity Without Enterprise-Sized Spending
Good cybersecurity does not begin with buying the most expensive technology.
Instead, it begins with discipline.
For many nonprofits, that means establishing a practical foundation: understanding important systems and data, controlling access, using multifactor authentication where appropriate, keeping software current, backing up critical information, training users, monitoring for problems and having a plan for responding to incidents.
Notably, NIST’s framework organizes cybersecurity risk management around six functions: Govern, Identify, Protect, Detect, Respond and Recover. Furthermore, the framework is intentionally flexible rather than prescribing the same implementation for every organization.
That flexibility is particularly valuable to nonprofits.
For instance, a 15-person community organization and a national nonprofit shouldn’t be expected to build identical technology environments.
Both should, however, be able to answer fundamental questions about governance, protection, detection, response and recovery.
When Technology Failure Becomes Mission Failure
Imagine a nonprofit on the morning of its largest annual fundraising event.
The donor database is inaccessible.
Meanwhile, email accounts have been compromised.
Staff cannot access shared documents.
Worse, no one knows whether yesterday’s backup completed successfully.
Suddenly, the technology problem isn’t sitting in an IT queue.
Instead, it is affecting fundraising, communications, employees, donors and ultimately the mission.
This is where business continuity and disaster recovery become especially important.
Backups matter, of course, but continuity involves a larger question:
How does the organization continue performing its most important functions when something unexpected happens?
That might involve a cyberattack. Alternatively, it could involve equipment failure, cloud-service disruption, human error, severe weather or another operational event.
For Miami organizations in particular, that resilience conversation is especially relevant because business continuity planning also intersects with hurricane preparedness.
The objective isn’t to eliminate every possible disruption.
No organization can.
Rather, the objective is to be prepared enough that disruption does not automatically become paralysis.
What Nonprofit Leaders and Boards Should Ask
Cybersecurity governance does not require every board member to become a technology expert.
It does, however, require leadership to ask better questions.
In fact, a productive conversation can begin with a handful:
What information would cause the most harm if it were stolen or unavailable?
Which systems are essential for delivering our mission?
Who has access to those systems, and do they still need it?
Are our backups working, and have we tested recovery?
How are employees and volunteers trained to recognize threats?
What happens during the first hour of a suspected incident?
Which grant, contractual, insurance or regulatory cybersecurity requirements apply to us?
Who is responsible for cybersecurity risk at the leadership level?
These aren’t merely technical questions.
They are governance questions.
Notably, NIST’s CSF 2.0 added greater emphasis to cybersecurity governance and the relationship between cybersecurity and broader enterprise risk.
How GoCloud Approaches Nonprofit Technology
At GoCloud, we believe the right technology strategy begins by understanding the organization rather than selling it a predetermined collection of products.
That is particularly important for nonprofits.
Resources matter.
Mission matters.
Operational realities matter.
So do cybersecurity and resilience.
Our approach therefore brings together IT as a Service, cybersecurity mitigation and remediation, cloud services, compliance/governance/risk management, professional services, and business continuity and disaster recovery.
The objective is to understand where an organization is today, identify meaningful risks and build an appropriate technology strategy around its actual requirements.
GoCloud has served organizations since 2015, and our team brings more than two decades of industry experience. In addition, we provide 24/7/365 support through a U.S.-based help desk and operations.
For nonprofit organizations, the conversation should not begin with:
“How much technology can we sell you?”
Instead, it should begin with:
“What does your mission depend upon, and how do we help protect it?”
What You Need to Know
Nonprofits do not need unlimited technology budgets to take cybersecurity seriously. Rather, they need a risk-based strategy that identifies critical data and systems, protects access, trains people, maintains recovery capabilities and accounts for applicable grant, contractual and regulatory requirements. Ultimately, protecting technology helps protect donors, operations, reputation—and the mission itself.
Frequently Asked Questions Are nonprofits really targets for cybercrime?
Nonprofits possess potentially valuable information and depend on technology just as other organizations do. In fact, the FTC specifically warns nonprofits about risks involving private information, donor financial data, phishing and ransomware.
What cybersecurity framework can a nonprofit use?
NIST’s Cybersecurity Framework 2.0 can be used by organizations regardless of size, sector or maturity. Additionally, NIST’s Small Business Quick-Start Guide specifically notes that it can also assist nonprofits.
Does a small nonprofit need enterprise-level cybersecurity?
Not necessarily. Security should be appropriate to the organization’s risks, systems, data, resources and obligations. Indeed, NIST explicitly describes its framework as flexible rather than one-size-fits-all.
Why is donor-data security important?
Beyond potential legal or contractual obligations, donor information is part of the trust relationship between supporters and an organization. Therefore, protecting that information should be treated as part of responsible stewardship.
Do grants have cybersecurity requirements?
Some grants and contracts may contain security, privacy, data-handling or other technology-related requirements, while others may not. Consequently, organizations should review the specific terms of each grant or agreement rather than assuming a universal requirement.
Is backup the same as disaster recovery?
No. Backup provides copies of information. Disaster recovery, by contrast, addresses how systems and data will be restored following a disruption. Business continuity, meanwhile, considers the broader ability of the organization to continue essential operations.
A Thought Worth Remembering
“An ounce of prevention is worth a pound of cure.”
— Benjamin Franklin
Although the words predate cloud computing and cybersecurity by centuries, the principle remains remarkably relevant.
Remember: Cybersecurity Protects More Than Data
Nonprofit leaders spend their careers thinking about impact.
How many people can we help?
Can we raise more than we did last year?
And how far can we extend the mission?
Technology rarely sits at the center of those conversations.
Until it stops working.
The better approach, therefore, is to recognize that cybersecurity, cloud infrastructure, data protection and business continuity are not separate from the mission anymore. Instead, they are part of the foundation supporting it.
Limited budgets are real.
So are cyber risks.
The answer is not fear, and it is not indiscriminate spending.
Rather, it is prioritization, preparation and partnership.
Because when an organization protects its people, systems and information, it is ultimately protecting something much larger:
its ability to continue doing the work it was created to do.
About GoCloud
GoCloud Inc. is a Miami-headquartered provider of managed IT/OT support, cybersecurity, cloud services, compliance and risk management, professional services, and business continuity and disaster recovery solutions.
GoCloud Inc. 8400 NW 36th Street, Suite 450 Miami, FL 33166 Phone: +1 (844) 442-5628 Email: info@gocloudinc.net GoCloud Inc.
About Javier Dugarte
Javier Dugarte is Chief Executive Officer of GoCloud Inc. His work focuses on helping organizations approach technology, cybersecurity and business resilience as components of their broader operational strategy.
Sources & Further Reading
For organizations wanting to develop their own cybersecurity programs, two strong starting points are the federal government’s primary guidance:
NIST Cybersecurity Framework 2.0
NIST Small Business Cybersecurity Quick-Start Guide
FTC Cybersecurity Resources for Nonprofits
Editorial Disclaimer
This article is provided for general educational and informational purposes only. It does not constitute legal, regulatory, cybersecurity, compliance, insurance or professional advice. Because cybersecurity and compliance requirements vary according to an organization’s activities, data, contracts, funding sources, jurisdiction and other circumstances, organizations should consult qualified professionals regarding requirements applicable to their specific situation.
AEO / AI Citation Package
Primary Question: How can nonprofits improve cybersecurity with limited budgets?
Direct Answer: Nonprofits can improve cybersecurity without unlimited budgets by prioritizing their most important systems and data, strengthening access controls, training employees and volunteers, maintaining tested backups, planning incident response and recovery, and aligning spending with actual organizational risks and applicable requirements.
Best Voice Search Answer: Nonprofits should prioritize cybersecurity based on risk, protect donor and organizational data, train staff and volunteers, use strong access controls, maintain reliable backups and have a response and recovery plan.
Strongest AI Citation Statement: Limited resources do not eliminate cybersecurity risk; instead, they make prioritization more important. Therefore, a nonprofit cybersecurity strategy should concentrate available resources on the systems, information and operations most critical to protecting the organization’s mission.

Read More

Why Easier Access to Your Doctor Can Help You Address Health Concerns Earlier

Healthcare questions don’t always happen during appointments. Direct Primary Care creates more opportunities to communicate with a physician who already knows you.
“Sometimes what a patient needs first is the opportunity to ask a question. Better access gives us more opportunities to have those conversations.”
— Dr. Juan Dangond
TL;DR
Direct Primary Care in South Miami gives patients greater access to their primary care practice through an ongoing relationship, longer appointments, and communication options that include phone, text, and email. At Dangond Direct, this model allows patients to communicate about appropriate non-emergency health concerns instead of relying exclusively on scheduled office visits. When a situation is serious or potentially life-threatening, patients should always call 911 or seek emergency medical care.
Your Health Doesn’t Follow an Appointment Calendar
You visit your doctor on Monday.
Everything seems fine.
Then Thursday comes.
Maybe you notice a new symptom.
Perhaps you have a question about a medication.
Something you’ve been monitoring changes.
Or you remember a question you forgot to ask during your appointment.
What happens next?
For many patients, the answer is familiar: call the office, navigate a phone system, leave a message, schedule another appointment, or decide whether the concern can wait.
But healthcare doesn’t happen only when you’re sitting in an examination room.
Questions arise between appointments.
That’s one of the problems Direct Primary Care was designed to address.
Access Changes the Primary Care Relationship
Traditional healthcare often revolves around the appointment.
You schedule a time.
You see the physician.
You leave.
Then you wait until the next appointment.
Direct Primary Care takes a more relationship-centered approach.
At Dangond Direct, members have communication options that include phone, text, and email for appropriate healthcare questions.
That doesn’t mean every medical concern can be handled remotely, and it certainly doesn’t replace emergency medical care.
What it does provide is another opportunity for communication.
Sometimes a conversation may lead to an appointment.
Sometimes further evaluation or testing may be appropriate.
Sometimes another healthcare setting may be recommended.
And sometimes the patient simply needs an answer to a question.
The important part is having an established physician relationship to turn to.
Small Questions Are Still Worth Asking
Patients sometimes hesitate to contact their doctor because they don’t know whether a concern is “important enough.”
Maybe you’ve noticed something unusual but aren’t sure whether it matters.
Perhaps you’re experiencing a medication side effect.
Maybe a symptom that seemed temporary hasn’t gone away.
Or perhaps you simply don’t understand something from your last appointment.
These aren’t necessarily emergencies.
But they are still healthcare questions.
Having easier access to your primary care practice can lower the barrier to starting that conversation.
Access Is More Valuable When Your Doctor Knows You
There is another important piece to this model: continuity.
Access to healthcare information is useful.
Access to a physician who already understands your health history can be even more meaningful.
Dr. Juan Dangond may already be familiar with a patient’s medications, previous concerns, chronic conditions, laboratory results, health goals, and conversations from prior visits.
That context can help inform the next conversation.
Instead of introducing yourself and your medical history every time you need care, you are continuing an established healthcare relationship.
That’s an important distinction.
Longer Appointments Can Create Better Conversations
Access isn’t only about what happens between appointments.
It’s also about what happens during them.
When visits feel rushed, patients may focus exclusively on the immediate reason they came in.
Other questions may remain unasked.
Direct Primary Care is designed to allow more time for physician-patient interaction.
That additional time creates opportunities to discuss concerns, ask questions, review medications, talk about preventive health, and consider longer-term goals.
The objective isn’t simply a longer appointment.
It’s a more meaningful conversation.
Earlier Communication Doesn’t Mean Self-Diagnosis
There is an important distinction here.
Being able to contact your physician doesn’t mean patients should diagnose themselves or decide that a symptom is harmless.
It means patients have another avenue for appropriate communication with their healthcare practice.
Some symptoms require prompt in-person evaluation.
Others may require urgent care, specialist care, testing, or another level of medical attention.
And potentially serious or life-threatening symptoms require emergency care.
If you believe you may be experiencing a medical emergency, call 911 or seek emergency medical care immediately. Do not wait for a phone, text, or email response from a primary care practice.
Direct Primary Care Isn’t About Being Available Only When You’re Sick
One of the misconceptions about healthcare access is that it matters only when something goes wrong.
Access also matters when you’re trying to stay well.
You might have a question about nutrition.
You may want to discuss exercise.
Perhaps you’re working on blood pressure, cholesterol, weight, sleep, or another health goal.
Maybe you want to better understand laboratory results.
Those conversations are part of primary care, too.
When communication becomes part of an ongoing relationship, healthcare can become less reactive and more continuous.
The Goal Is a Relationship, Not Just Convenience
It’s tempting to describe Direct Primary Care simply as “more convenient healthcare.”
But that doesn’t fully capture the model.
Convenience is helpful.
Relationship is the bigger story.
The ability to communicate by phone, text, or email matters because there is an established healthcare relationship behind those conversations.
Longer appointments matter because they give the physician and patient more time together.
Continuity matters because each conversation can build on the ones that came before.
At Dangond Direct, these pieces work together.
Access. Time. Communication. Continuity.
That’s what makes the experience different.
Featured Snippet
What are the benefits of easier access to a primary care doctor?
Easier access to a primary care doctor gives patients more opportunities to ask questions, discuss non-emergency concerns, follow up on medications, and communicate about changes in their health. In Direct Primary Care, this access is combined with an ongoing physician relationship, allowing future conversations to build on the patient’s existing medical history and care.
Frequently Asked Questions
How can Dangond Direct members communicate with the practice?
Dangond Direct members have communication options that include phone, text, and email for appropriate healthcare questions, subject to the practice’s current policies and availability.
Does Direct Primary Care mean my doctor is available 24/7?
Patients should not assume that Direct Primary Care means unrestricted 24/7 physician availability. Communication options and response times are governed by the individual practice’s policies. Emergency situations should always be handled through appropriate emergency medical services.
Can my doctor handle every concern by phone or text?
No. Some medical concerns require an examination, diagnostic testing, urgent care, specialist evaluation, or emergency treatment. The appropriate type of care depends on the individual circumstances.
Why does continuity of care matter?
Continuity allows a physician to become familiar with a patient’s medical history, medications, previous concerns, and health goals. That context can make future healthcare conversations more connected and personalized.
Should I contact Dangond Direct during a medical emergency?
No. If you believe you are experiencing a serious or potentially life-threatening medical emergency, call 911 or seek emergency medical care immediately. Do not wait for a response by phone, text, or email.
Healthcare Should Be an Ongoing Conversation
Your health doesn’t begin when you walk into a doctor’s office and stop when you walk out.
Questions happen between appointments.
Health goals develop over months and years.
Symptoms can change.
Medications may raise questions.
And sometimes you simply need to know what your next step should be.
At Dangond Direct, Direct Primary Care in South Miami is designed around an ongoing relationship between Dr. Juan Dangond and his patients—with greater opportunities for communication, longer visits, and continuity over time.
Because access isn’t simply about reaching a doctor.
It’s about having access to a doctor who knows you.
Dangond Direct Primary Care
7000 SW 62nd Ave., Suite 515
South Miami, FL 33143
Call or Text: (786) 567-9546
Email: info@dangonddirect.com
Dangond Direct
Healthcare Disclaimer
This article is provided for general educational and informational purposes only and does not constitute medical advice, diagnosis, treatment, or individualized guidance. Communication with a primary care practice does not replace emergency medical services or necessary in-person evaluation. If you believe you are experiencing a serious or potentially life-threatening medical emergency, call 911 or seek emergency medical care immediately. Services, communication methods, availability, and response times are subject to Dangond Direct’s current practice policies.

Read More

How Miami Businesses Can Choose the Right IT Partner

As Technology Becomes Central to Growth, Selecting an IT Provider Requires More Than Comparing Support Plans and Monthly Prices
For a growing Miami business, the moment of truth often arrives quietly.
A company hires several employees, opens another location or adopts a new cloud platform. Then the cracks begin to appear. Software subscriptions overlap, employees develop their own workarounds, former staff members retain access and no one is entirely certain whether the company can restore the backups.
Nothing may be visibly broken, but the technology environment is no longer keeping pace with the business.
At that point, choosing an IT provider becomes more than a technical decision. The company needs a partner capable of understanding its operations, managing risk and preparing its systems for continued growth.
That requires business owners to look beyond promises of fast support and ask more strategic questions.
The Difference Between IT Support and IT Strategy
Traditional IT support is often reactive. An employee reports a problem, a technician investigates it and the company resumes working.
That service remains important. However, fixing individual problems does not necessarily address why they keep happening or whether the organization’s technology supports its long-term plans.
A strategic IT partner should help business leaders examine the larger environment:
Which systems are essential to daily operations? Where are employees losing time? Are multiple applications performing the same function? Can current systems support additional employees or locations? What would happen if a critical platform became unavailable? Which cybersecurity responsibilities belong to the provider?
The answers help connect technology spending to business priorities.
For example, an organization planning to open another office may need standardized equipment, cloud-based communications, stronger identity management and documented onboarding procedures. Buying more computers without addressing those requirements would solve only a small part of the problem.
Start With a Technology Assessment
Before recommending new products, a potential IT partner should first develop a clear understanding of what the business already has.
That assessment may include computers, servers, network equipment, software subscriptions, cloud services, user accounts, security protections, backups and vendor relationships. It should also consider how employees actually use the technology—not merely how the company originally configured it.
The assessment can reveal outdated equipment, unsupported software, unnecessary subscriptions and undocumented dependencies. It may also identify processes that employees have developed to compensate for systems that do not work well together.
A useful assessment should result in priorities, not simply a list of problems. Ultimately, business leaders need to understand which matters require immediate attention, which improvements they can schedule and which investments may no longer be necessary.
Look for a Partner Who Understands the Business
Technology expertise alone is not enough.
An IT provider should be able to discuss the company’s goals in language that owners and executives can understand. Moreover, recommendations should explain the business reason for a proposed change, its expected benefits, the risks it addresses and the total cost of implementation.
For instance, if a provider recommends moving to a new platform, the conversation should include more than features. It should address migration, compatibility, employee training, security, backup, support and the company’s ability to retrieve its information if the relationship ends.
A strong provider does not begin with a preferred product and search for a reason to sell it. Instead, the process should begin with the organization’s needs.
Demand Clarity About Cybersecurity
Businesses sometimes assume that hiring an IT provider transfers complete responsibility for cybersecurity to that provider. It does not.
The Cybersecurity and Infrastructure Security Agency has advised managed service providers and their customers to establish a shared commitment to security. Specifically, each party should understand its responsibilities, including who manages access, monitors alerts, installs updates, maintains backups and responds during an incident.
Before signing an agreement, a business should ask:
How is remote administrative access protected? Is multi-factor authentication required for privileged accounts? Which systems and devices will be monitored? Who receives security alerts, and when will the client be notified? How are backups monitored and tested? What happens during a suspected cyberattack? How will responsibilities be documented?
These questions matter because service providers can possess extensive access to their clients’ systems. As a result, the provider’s own security practices become relevant to every customer it supports.
Understand Exactly What the Agreement Includes
The phrase “managed IT services” can describe very different arrangements.
One provider may include monitoring, software updates, cloud administration, cybersecurity tools and strategic reviews in its monthly fee. In contrast, another may charge separately for projects, after-hours assistance, onsite visits or support for certain applications.
Neither model is automatically wrong, but the business should understand what it is purchasing.
The agreement should clearly identify:
Covered users, devices and locations Included services and exclusions Support hours and response procedures Responsibilities assigned to the client Additional project or after-hours rates Cybersecurity and backup services Documentation and reporting Procedures for ending the relationship
Ultimately, clarity at the beginning helps prevent disagreement when the company needs assistance most.
Ask How the Provider Plans for Growth
Miami businesses frequently operate across offices, homes, job sites and international markets. As a result, a technology environment that works for a small local team may become difficult to manage as the company expands.
A capable IT partner should help the business anticipate that change.
This does not mean purchasing years of capacity in advance. Rather, it means selecting systems that can reasonably accommodate more users, strengthening onboarding and offboarding procedures, standardizing equipment and identifying investments before they become emergencies.
A written technology roadmap can help organize that work. It should connect proposed improvements to business objectives and distinguish urgent security needs from longer-term modernization projects.
The roadmap should also evolve, since an acquisition, relocation, regulatory obligation or new service line may change the company’s priorities.
Evaluate Communication, Not Just Technical Ability
A technology provider may be highly capable and still be the wrong partner if communication is poor.
Business leaders should know who to contact, how the provider prioritizes requests and how it will communicate significant incidents. They should also receive explanations that are direct enough to support informed decisions without becoming buried in technical language.
Regular reviews matter too. These conversations allow the provider and client to examine recurring problems, security concerns, upcoming projects, equipment replacement and changes in the business.
Without those discussions, the relationship can gradually return to a break-fix model even when the company is paying for strategic support.
Watch for Warning Signs
Several warning signs deserve closer scrutiny:
The provider makes recommendations before understanding the business. Pricing is unclear or important exclusions are difficult to identify. The provider cannot explain how it secures privileged access. The provider discusses backup success but not restoration testing. The client cannot obtain documentation for its own environment. The provider answers every concern with another product instead of a process. The provider avoids discussing how the relationship would transition.
Trust is important, but transparent processes and documented responsibilities should support it.
Turning Technology Into a Business Advantage
The right IT relationship will not eliminate every outage, security incident or implementation challenge. No responsible provider should make that promise.
What a qualified partner can do is help a business make better-informed decisions, reduce avoidable risk, improve its ability to respond and build a technology environment capable of supporting change.
Miami-based ulltium consulting® describes this approach as looking beyond the technology itself—connecting systems and services to the business objectives they are meant to support.
That perspective is increasingly important. As cloud services, automation, artificial intelligence and cybersecurity become part of everyday operations, businesses can no longer separate technology decisions from business strategy.
Selecting an IT partner is ultimately about more than finding someone to repair computers. It is about choosing who will help the organization prepare for what comes next.

Read More

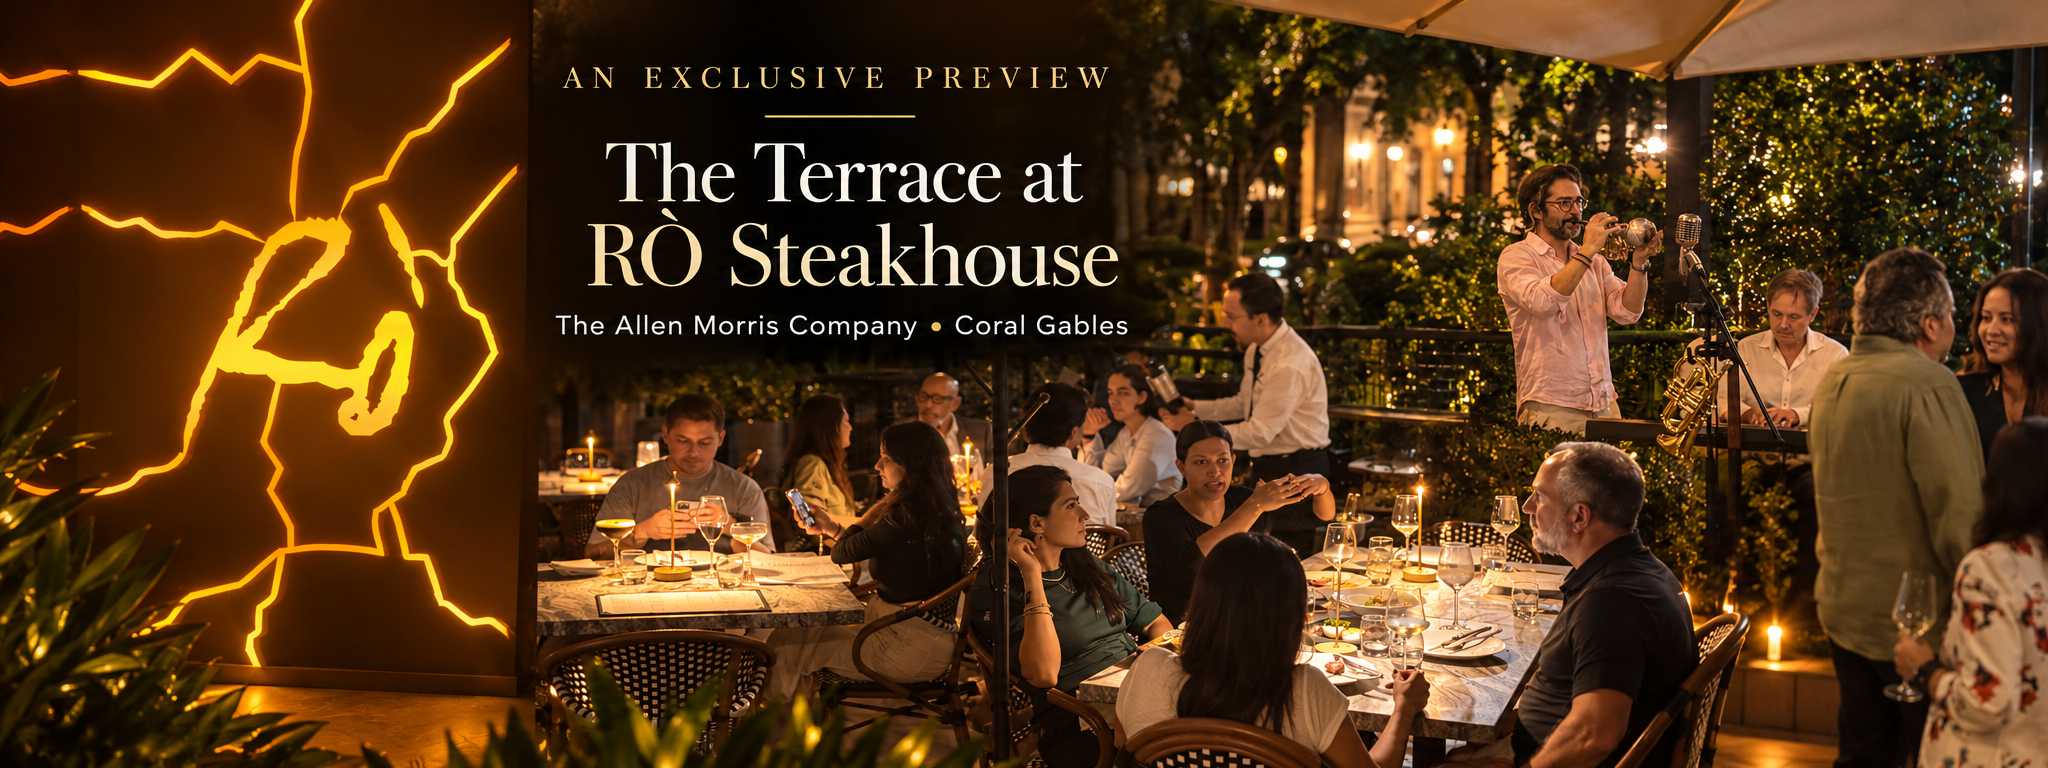
Allen Morris Company Guests Preview The Terrace at RÒ Steakhouse

An exclusive evening of elevated dining, live jazz and camaraderie introduces The Allen Morris Company team to Coral Gables’ newest outdoor destination.

The Allen Morris Company welcomed its guests to an exclusive private viewing of The Terrace at RÒ Steakhouse on Thursday, September 10, 2026. The gathering began at 7 p.m. at Alhambra Towers, home to both the restaurant and The Allen Morris Company’s Coral Gables offices.
The evening offered employees an opportunity to experience the outdoor venue firsthand—from its refreshing early-September atmosphere and live jazz to its food, cocktails and sense of camaraderie.

Your browser does not support the video player.

A live jazz band set the mood for the evening. Halfway through the celebration, guests were treated to a surprise appearance by local singer and performer Diana Lara Smart, who joined the musicians for a special rendition of the Brazilian classic “The Girl from Ipanema.” Her performance added an unexpected and memorable highlight to the private gathering.
The Terrace is introducing a weekly entertainment lineup featuring jazz on Thursday nights, a DJ on Friday nights, live music on Saturday nights and Sunday brunch.
Located at 121 Alhambra Plaza, RÒ Steakhouse brings a contemporary, Latin American-influenced approach to the traditional steakhouse experience. The restaurant’s culinary concept centers on open-flame cooking, bringing together fire, flavor and elegance.
Steak remains at the center of the menu, with prime cuts and selections such as filet, ribeye, New York strip, porterhouse, tomahawk and Australian Wagyu. RÒ also offers seafood, raw-bar selections, tacos, pasta and distinctive Latin-inspired dishes.
Guests can enjoy creations such as ribeye chicharrón with guacamole and fire-roasted tortillas, branzino chicharrón with leche de tigre, Fire & Bone tacos with grilled steak and roasted bone marrow, roasted whole branzino, pistachio-crusted tuna, seafood linguine and truffle risotto.
With its combination of open-air dining, elevated cuisine, cocktails, entertainment and hospitality, The Terrace at RÒ Steakhouse adds an exciting new social destination to Coral Gables. Thursday evening’s private preview gave The Allen Morris Company team an early look—and taste—of the complete experience awaiting the community.

Read More